The establishment of the Data Protection Board of India was expected to be a significant step towards giving practical effect to India’s new data protection framework. However, the distinction between establishing a statutory authority and making it operational raises an important question: can a data protection framework effectively protect individual rights when the institution entrusted with its enforcement is not yet functional?
This question has acquired particular significance following the order of the Kerala High Court in C.R. Neelakandan v. Union of India, WP(PIL) No. 15 of 2026, dated 7 October 2026.
Establishment and functioning are two different things
Section 18 of the Digital Personal Data Protection Act, 2023 provides for the establishment of the Data Protection Board of India by the Central Government. The Board is intended to function as the principal statutory authority responsible for examining complaints, inquiring into personal data breaches and exercising the powers conferred upon it by the Act.
The Central Government issued G.S.R. 844(E) dated 13 November 2025 to establish the Board. Separately, G.S.R. 845(E), issued on the same date, provides that the Board shall consist of four members.
These notifications establish the institutional framework. They do not, by themselves, establish that the Board has the personnel, administrative arrangements and operational capacity necessary to discharge its functions.
This distinction is not merely administrative. A statutory body may exist in law, but its ability to perform its statutory responsibilities depends upon the availability of its members, supporting staff, procedural arrangements and the necessary infrastructure.
What did the Kerala High Court observe?
The issue came before the Kerala High Court in C.R. Neelakandan v. Union of India. The proceedings concerned privacy issues arising from the handling of passenger information at airports, including the Digi Yatra system.
During the proceedings, the Central Government’s counsel informed the Court that the Data Protection Board had been constituted under the DPDP Act but had not yet been made functional.
The Court recorded this submission and observed that, considering the purpose for which the DPDP Act had been enacted, it expected the Board to become functional within eight weeks.
The significance of this observation lies in the recognition that the existence of a statutory institution is not sufficient if it cannot perform the functions for which Parliament created it.
It is equally important to understand the precise nature of the order. The Court recorded the Government’s submission and expressed an expectation regarding operationalisation. It did not hold that the Board had already become functional, nor did it decide the substantive legality of the Digi Yatra data-processing arrangements.
The statutory concern
Sections 18 and 19 deal with the establishment and composition of the Board. Section 20 deals with the salary, allowances and term of office of its Chairperson and members. The subsequent provisions address disqualifications, vacancies, proceedings and staffing.
These provisions collectively demonstrate that Parliament contemplated an institution with a defined composition and institutional structure.
Section 27, which deals with the powers and functions of the Board, is particularly important. It envisages the Board examining matters such as personal data breaches, complaints and references, subject to the statutory framework.
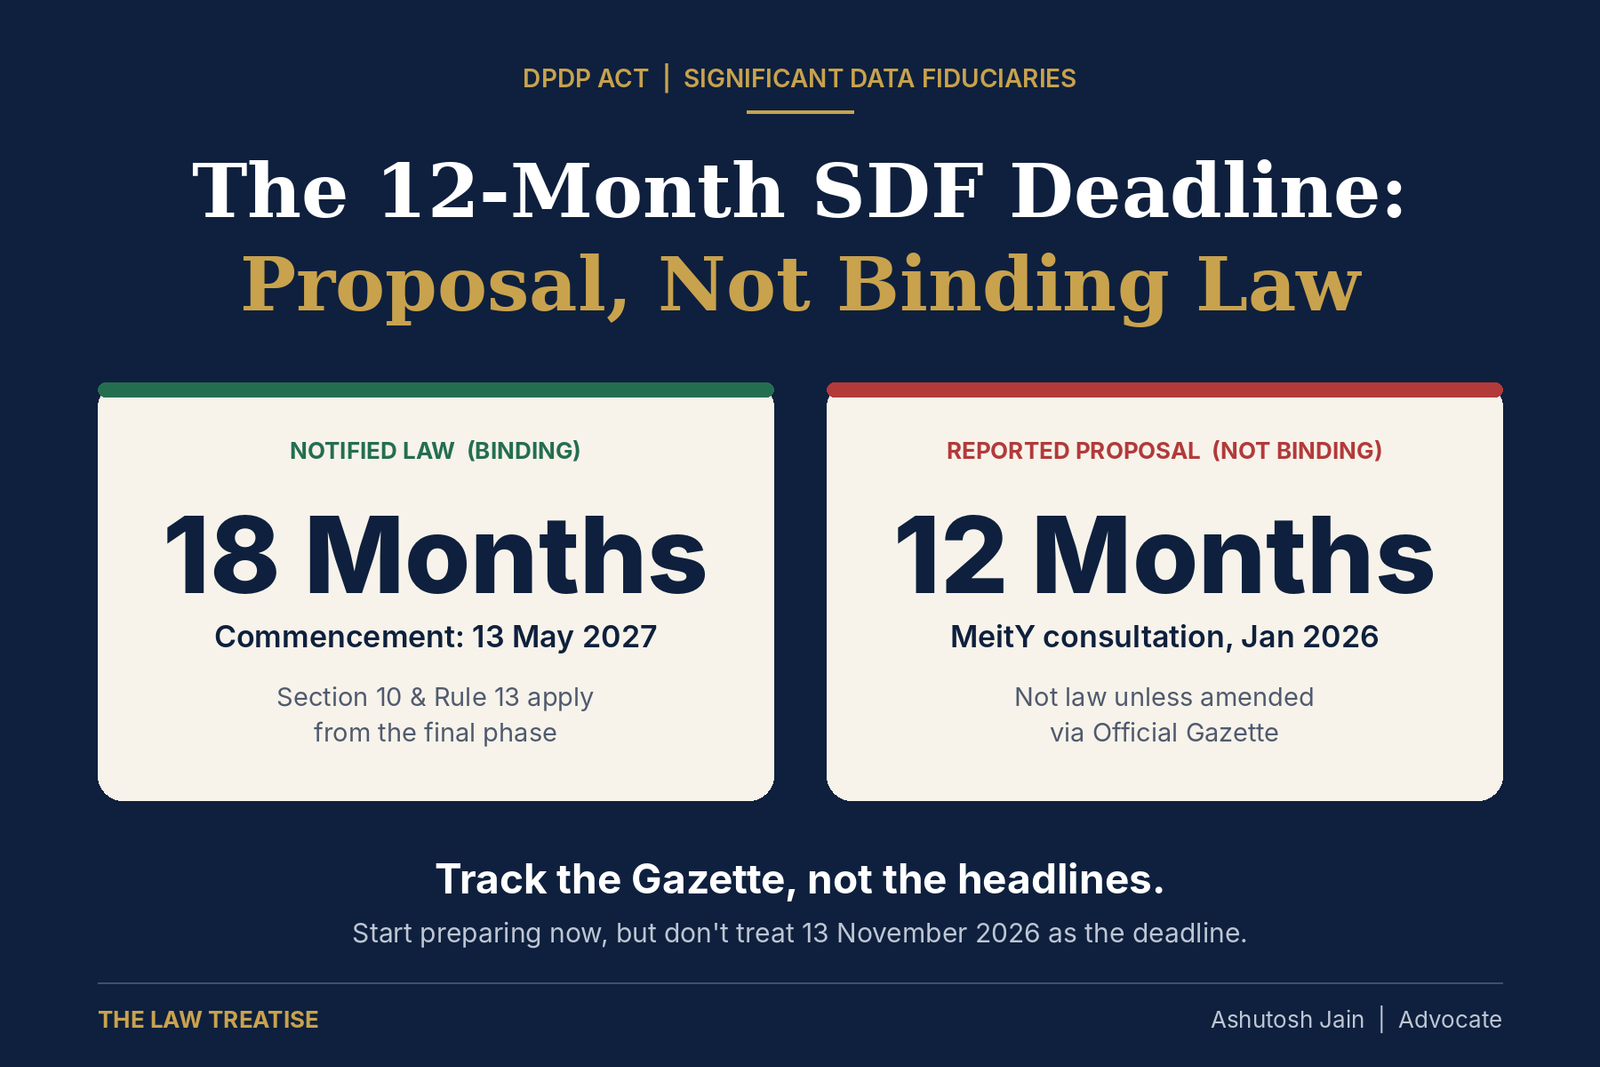
However, the commencement notification must also be considered. Under G.S.R. 843(E), section 27, except clause (d) of section 27(1), is scheduled to commence on 13 May 2027. Clause (d) commenced on 13 November 2026.
Consequently, the question of the Board’s functionality must not be confused with the commencement of every provision governing its adjudicatory functions.
Why does this matter to businesses?
For businesses, the absence of an operational regulator creates uncertainty in relation to the practical enforcement of the law.
A company may have questions concerning a personal data breach, the handling of a complaint, the interpretation of a regulatory requirement or the procedure for responding to an inquiry. An institution that has not commenced its operational functions cannot provide the same degree of regulatory engagement as a fully functioning authority.
However, this does not mean that businesses can disregard the statutory framework or postpone their compliance preparations.
A regulator’s operational status and a Data Fiduciary’s legal obligations are separate questions. Where the relevant substantive obligations have not yet commenced, the applicable commencement schedule must be considered. Equally, businesses should not assume that future enforcement arrangements will provide an excuse for inadequate security, poor documentation or weak internal governance.
The larger institutional question
The effectiveness of data protection legislation depends upon more than the quality of its statutory language. It also depends upon whether individuals can approach an independent authority and whether that authority can act within a meaningful period.
The Board is central to this institutional design. Its independence, staffing, accessibility and procedural efficiency will determine whether the statutory framework can translate into effective regulatory protection.
The Kerala High Court’s observation is therefore significant beyond the immediate facts of the case. It draws attention to an essential aspect of regulatory governance: a statutory institution must be capable of functioning, not merely exist in a Gazette notification.
The real test of India’s data protection framework will not be the notification establishing the Board, but its ability to discharge the responsibilities entrusted to it by Parliament.